Defense Contracts, that include the handling of CUI, Require Cybersecurity Certification.
The best time to start this process was a year ago. The second-best time to start is today.
Pilot Systems guides you from gap analysis to certification-readiness, in a fraction of the time it takes most firms to figure it out on their own.
On July 13th, 2026, the DoW announced a 60-day pause on the requirement of 3rd party assessment to achieve NIST/CMMC Compliance.
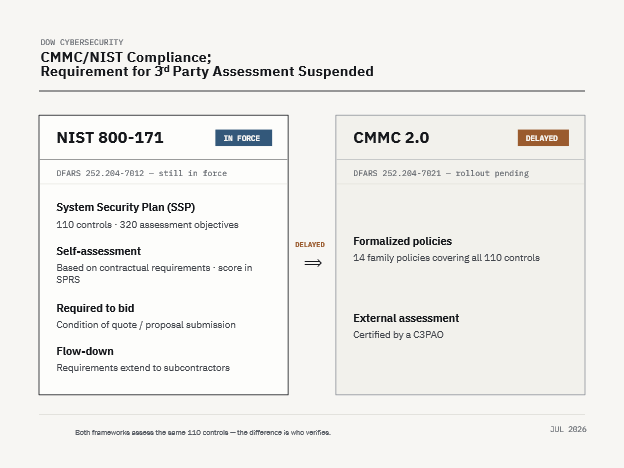
- The need for an experienced and qualified NIST/CMMC services provider has been increased with this suspension and the increasing activity of Whistle Blowers.
- Pilot recommends that self-assessing companies have the 3rd party assessment to mitigate the increased vulnerability of the signer of the company’s attestation. Pilot can provide this assessment.
Forty Years of Regulatory Compliance. NIST/CMMC Is the Newest Discipline.
Five Steps to NIST/CMMC Certification
1
2
3
4
5
If You Bid on and conduct DoW Contracts, This Applies to You.
If you handle CUI as part of a prime contractor relationship, your prime is already asking when you will be certified. We have decades of experience working alongside Tier 1 and Tier 2 organizations and understand how compliance work fits into a busy supplier operation.
Many of our long-standing automotive clients are exploring or actively bidding on DoW contracts as defense electrification, ground vehicle modernization, and autonomous systems programs expand. We can guide the same companies we have known for years through this new regulatory regime.
Companies with 50 to 500 employees often have the technical capability to comply but lack the dedicated compliance staff to execute. We provide that staff for the duration of your NIST/CMMC project — and only for the duration of your NIST/CMMC project.
Common Questions
Six to nine months from kickoff to a passed self or C3PAO assessment, depending on your starting security posture and your availability to support the NIST/CMMC L2 process. Companies with mature IT security programs, available internal staff (e.g., IT personnel) and existing NIST 800-171 alignment can move faster. Companies starting from scratch should plan on the full nine months.
NIST/CMMC engagements vary based on company size, system complexity, and remediation scope. The cost is affected by current readiness, your availability to support the processes, the boundary conditions of Cyber Security effected areas, and post assessment (carry on) services. We provide a fixed-fee scope after the initial scoping conversation, so you know what you are committing to before signing anything.
No — by federal mandate, 3rd party certification audits must be performed by an independent Certified Third-Party Assessment Organization (C3PAO). We prepare you for self-assessment or that audit. We can recommend C3PAOs we have worked with successfully; Pilot will stay engaged through the audit itself to support evidence requests.
We work to ensure that does not happen. Our process is built around preparing you so thoroughly that the C3PAO audit is confirmation, not discovery. If a finding does emerge during assessment, we help you build a corrective action plan and reset. With proper (e.g., Pilot led and provided) preparation, this is rare. In our team’s 10-year history, every assessment has been successful.
If there is a reasonable possibility your business will bid on CUI related DoW contracts, in the next three years, directly or as a subcontractor to a prime, the answer is yes. NIST/CMMC certification takes months, not weeks, and most companies discover the certification requirement too late to act on it before a specific bid window. This can lead to a delay in the receiving of DoW related contracts.